LAB_OPERATIONS
Every box I've rooted, written up the way I wish more writeups were written: the failed paths, the aha moment, the exact payload, the privesc. No hand-waving. If something took me six hours, I say so.
KGF
Full white-box penetration test across two network segments. Multi-stage pivoting via SNMP enumeration, IMAPS credential extraction, R-services lateral movement, and SSH key exfiltration to achieve dual root access.
DEMON
Grey-box engagement: virtual host enumeration, Jenkins default-cred RCE via Groovy console, XLSX hash cracking, rbash escape, and GTFObins scp to root.
BLINDERS
Black-box OSINT engagement: username enumeration, Hydra FTP/SSH brute force, Sherlock Reddit OSINT, credential reuse discovery, and GTFObins ftp shell for root privilege escalation.
MR. ROBOT 1
robots.txt fsocity.dic dedup, WordPress brute force, theme editor RCE, MD5 cracking, and SUID nmap --interactive escalation. 3 keys captured.
WORLD-OF-WONDERSX
Custom multi-stage CTF: openstego on raptors.webp, pcap credential extraction, Burp Intruder clusterbomb login, PHP webshell upload, oracle.php SQL injection, and a second Throwit.php upload chain to sudo su root.
COLDDBOX
WPScan user enum, xmlrpc brute force, WordPress theme editor reverse shell, and SUID find GTFObins escalation to root.
NULLBYTE
Exiftool metadata steg on main.gif, Hydra HTTP form-post brute, sqlmap dump of the seth database, hash crack, SSH on port 777, and PATH hijack via SUID procwatch binary to root.
VULNCMS
Drupalgeddon2 remote code execution against a multi-CMS target, plaintext credential recovery from the web root, and journalctl GTFOBins privilege escalation to root.
LAMPIAO 1
Drupalgeddon2 RCE on port 1898, credential extraction from settings.php, SSH lateral movement, and DirtyCow (CVE-2016-5195) kernel exploit for root.
TR0LL 1
Anonymous FTP pcap forensics, web directory maze, Hydra SSH brute force, and writable root cron job hijack via cleaner.py.
BREAKOUT
enum4linux user enum, brainfuck-encoded password in HTML source, Usermin port 20000 shell, and tar capability (cap_dac_read_search) for root.
EARTH
Vhost enum (earth.local + terratest), XOR-encrypted admin password via CyberChef, command injection, ltrace + reset_root SUID privesc.
FUNBOXENUM
Exposed PHP mini file manager, PHPMyAdmin credential extraction, Hydra SSH brute force, and MySQL GTFOBins sudo escape to root.
MONEYBOX 1
Anonymous FTP image download, stegseek steganography to extract SSH credentials, and sudo python3 GTFObins one-liner to root.
KIOPTRIX 1
enum4linux SMB fingerprint, Samba 2.2.1a trans2open heap overflow via Metasploit, and direct root shell: zero privilege escalation required.
THALES 1
Tomcat manager login brute via Metasploit, msfvenom JSP WAR shell deployment for initial access, then world-writable backup.sh cron script hijack to root reverse shell.
JANGOW 01
dirb directory enum, busque.php command injection, MySQL credential reuse from wp-config.php, and overlayfs kernel exploit on a 4.4.0 box for root.
BOB 1.0.1
dev_shell.php filter bypass, breadcrumb credential trail across home directories, and GPG-encrypted login.txt cracked with HARPOCRATES passphrase to root.
DEATHNOTE
WordPress user enum, brainfuck-encoded SSH password, WAV file steganography decoded with CyberChef hex→base64, and sudo NOPASSWD escalation as kira to root.
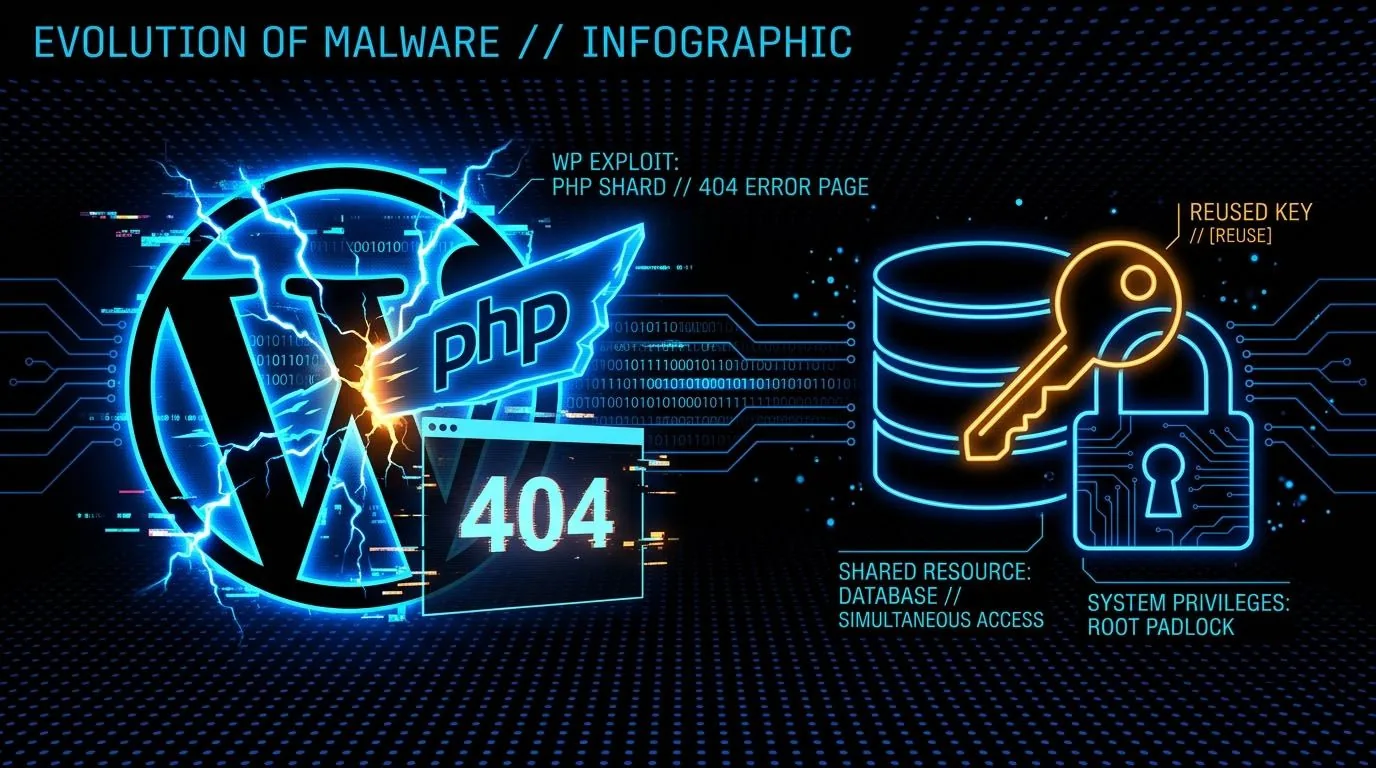
QUAOAR
WordPress admin:admin default credentials, theme editor 404.php reverse shell, and root access via wp-config.php database password reuse.
DRIPPING BLUES
Anonymous FTP zip download, fcrackzip rockyou crack, drip-parameter LFI to /etc/passwd and SSH key, and dpkg sudo GTFOBins postinst payload to root.
 HackTheBox